CSP Program Marketing Materials
This page is for Microsoft CSP partners who resell Token Watch through Microsoft Marketplace. It covers what the product does, who buys it, the answers to common security questions, list pricing, and logos and screenshots you can use in your own campaigns.
Marketplace listing Email the partner teamToken Watch at a glance
| Product | Token Watch |
|---|---|
| Category | Identity and security monitoring for Microsoft Entra ID |
| What it does | Monitors the client secrets and certificates on Entra ID app registrations and alerts the team before they expire |
| Offer type | SaaS, sold on Microsoft Marketplace |
| Typical users | DevOps, SRE, platform and cloud security engineers who run workloads on Azure |
| Access needed | One read-only Microsoft Graph permission, Application.Read.All, granted by an administrator |
| Setup | A few minutes: sign in with Microsoft and grant consent. Nothing is installed in the customer's tenant. |
| Support | By email in English. Standard requests answered within 48 hours, priority requests within 24. |
The problem customers have
Every app registration that signs in with a client secret or certificate has an expiry date. When one passes unnoticed, whatever uses it stops authenticating. That might be an API, a deployment pipeline or an integration with another company. The error is usually AADSTS7000222, and the first report often comes from a customer.
Microsoft Entra has no expiry alert you can set up for these credentials. Its closest feature is a preview recommendation that emails users in the Application Administrator role once, when credentials first fall within 30 days of expiry. It does not email the app's owner and it does not repeat. Most teams end up with a calendar reminder, a spreadsheet or a script that someone has to keep running.
What Token Watch does
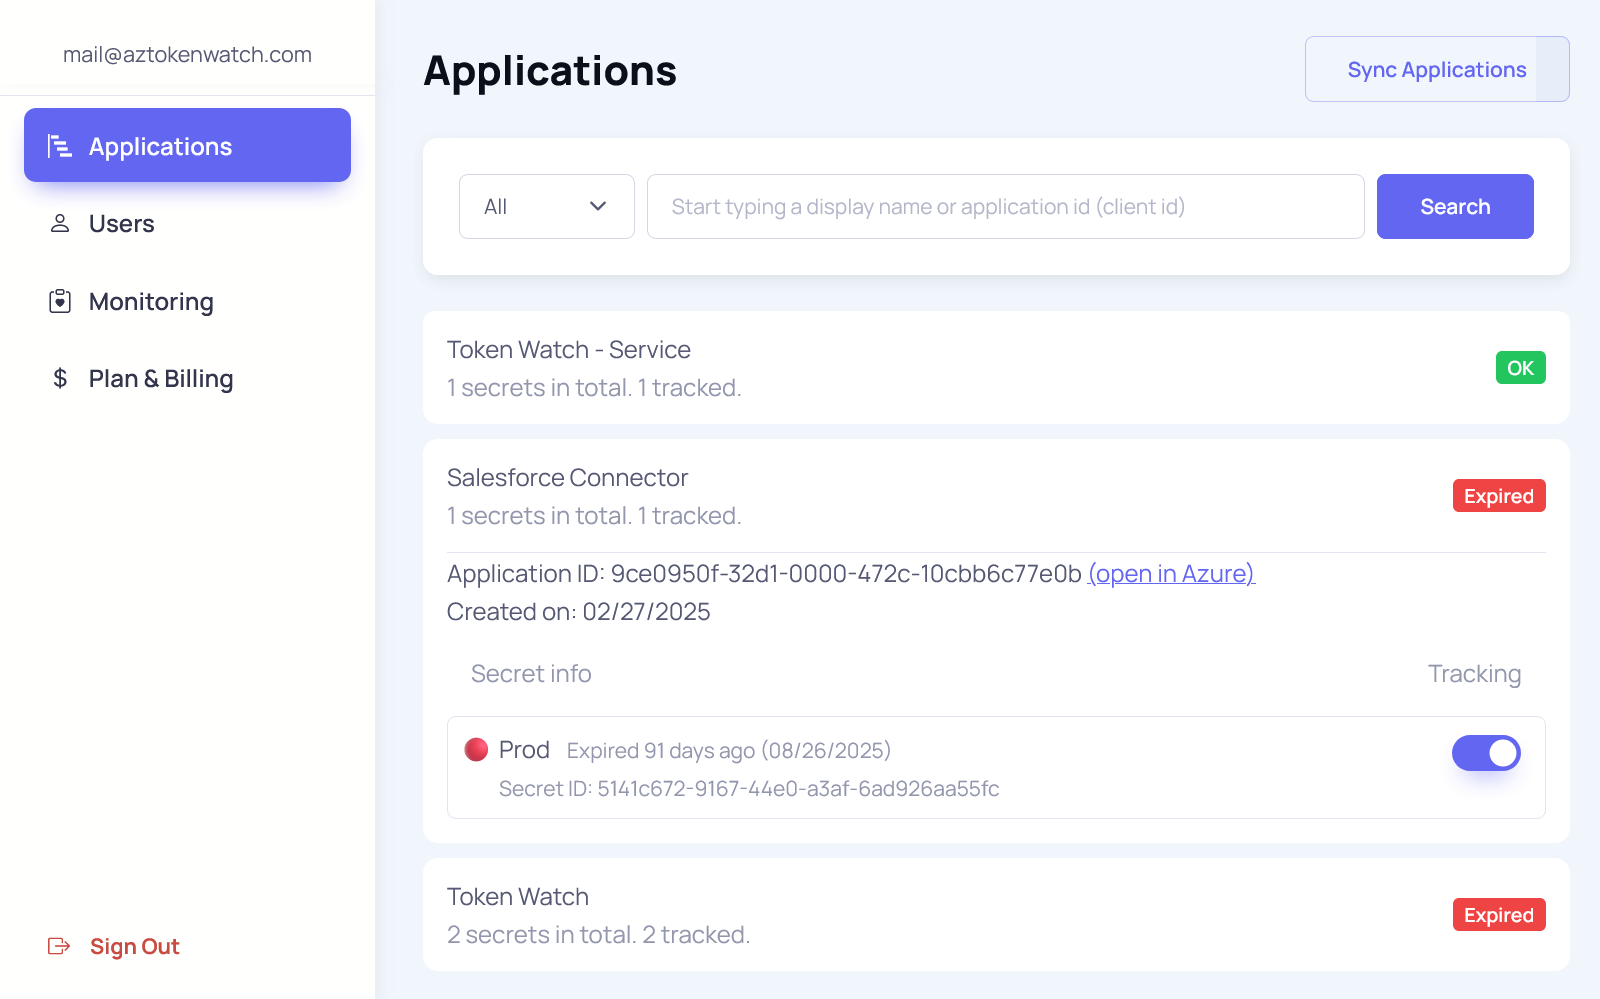
- Lists every app registration in the connected tenant, with the expiry status of each client secret and certificate.
- Checks the tenant every night at about 02:00 UTC and emails a daily report of expired and expiring credentials. Email alerts are included on every plan, Free too.
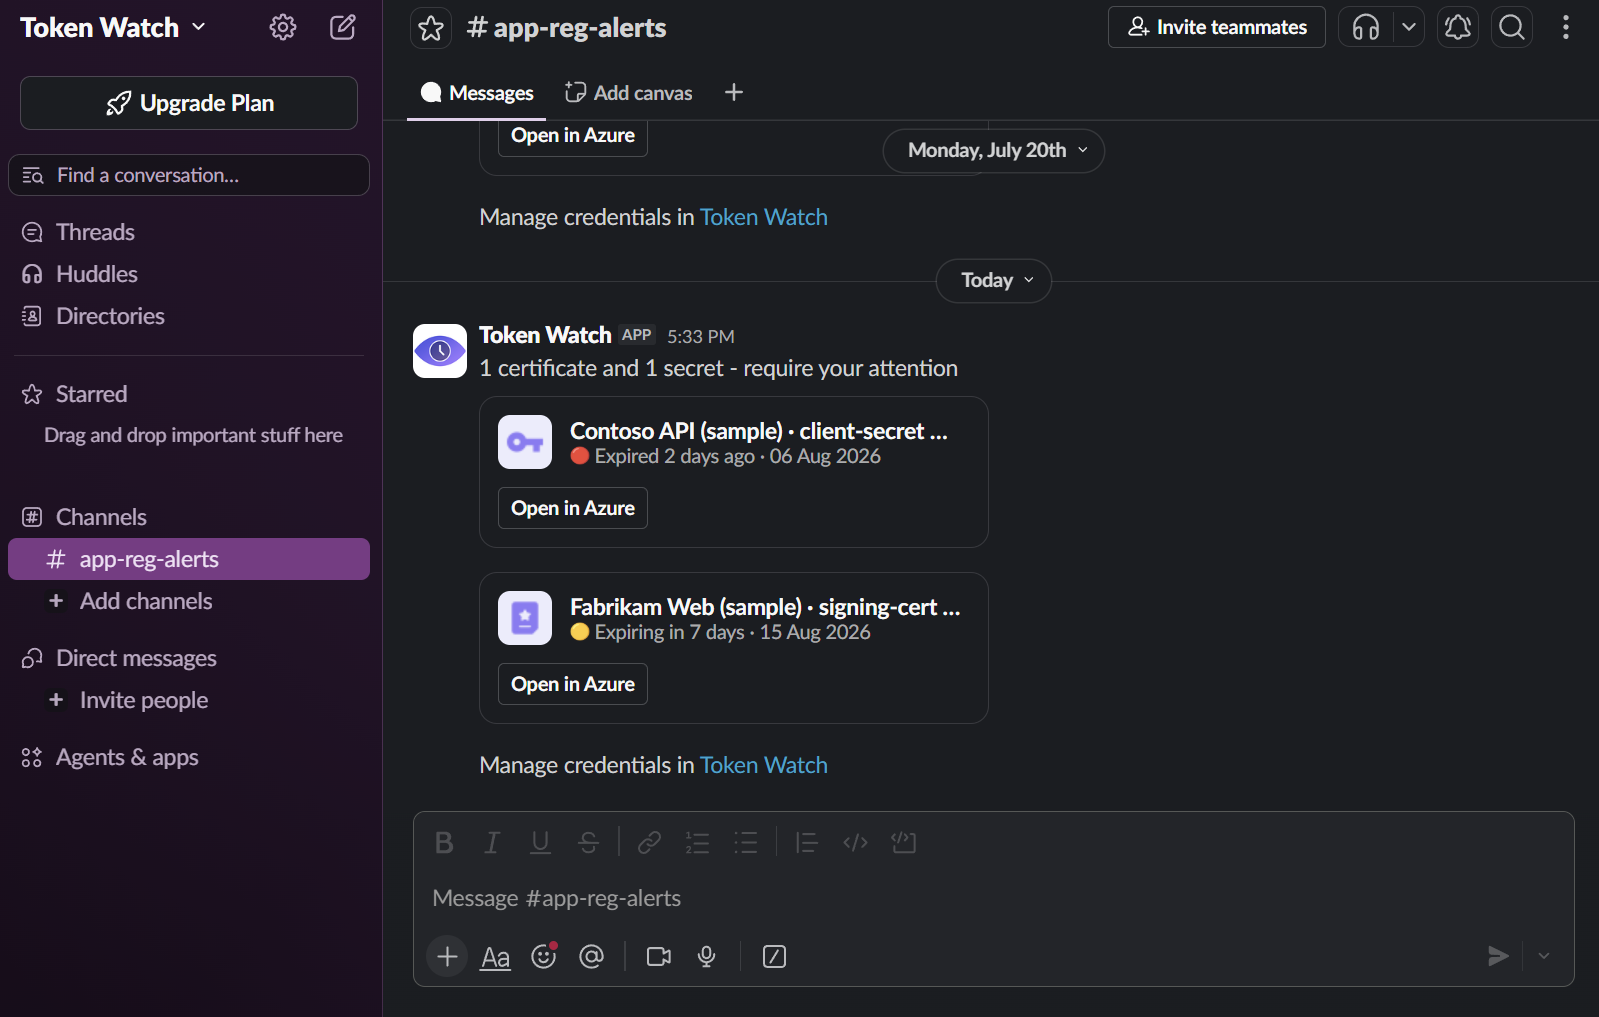
- On the Team plan, sends alerts to one more place alongside email: Slack, Microsoft Teams, Azure DevOps work items, or a signed custom webhook for PagerDuty, ServiceNow, Opsgenie and similar tools.
- Lets the team switch tracking off for individual credentials that nobody plans to rotate, so the alerts that remain are ones someone should act on.
- Exports the credential inventory to CSV on the Team plan.
Who to sell it to
Token Watch fits best where some of these are true:
- The tenant has dozens or hundreds of app registrations, and nobody has a full list of who owns which.
- An expired secret or certificate has caused an outage in the last year or two.
- Azure DevOps pipelines or GitHub Actions deploy through service principals that use secrets.
- The security or compliance team wants an inventory of application credentials and their expiry dates.
- The team maintains a homegrown PowerShell script or Logic App for expiry checks and would rather not.
The people who feel the pain are platform and DevOps leads, SREs and cloud security engineers. The budget usually sits with the head of platform, infrastructure or IT operations. List prices are low enough that a single team lead can often approve them.
Security questions you will hear
Security reviewers ask these before they approve tenant-wide consent. Full detail is in the security review pack, which you can send to the customer as is.
| Question | Answer |
|---|---|
| What can Token Watch access? | Application.Read.All as an application permission, used against a single Graph endpoint that lists applications. It has no write access. Details |
| Does it store secrets? | No. It stores metadata: application and credential names, IDs, start and expiry dates, and owner IDs. Field-by-field list |
| Is anything installed in our environment? | No. Token Watch calls Microsoft Graph from its own infrastructure, and nothing connects into the customer's network. |
| Where is the data hosted? | On Azure in the United States. EU hosting is available for enterprise customers who ask before sign-up. Architecture |
| Can we avoid storing app names and dates at all? | Yes, with no-persistence mode, arranged per tenant on request. Only bare identifiers are kept and everything else is read live from Graph. How it works |
| Is it SOC 2 or ISO 27001 certified? | No, and Token Watch does not claim to be. The controls those audits look at are mapped on the certifications page. If the customer's procurement requires a current certificate, Token Watch does not meet that requirement today. |
| How do we remove it? | Delete the Token Watch enterprise application in Entra ID. Access stops at once, with no notice period. Revoking access |
Plans and list prices
| Plan | List price | App registrations | Includes |
|---|---|---|---|
| Free | $0 | Up to 100 | Full inventory and email alerts from three business days before expiry, with no time limit |
| Starter | $29 / month | Up to 200 | Configurable warning period, alerts until resolved, multiple recipients |
| Team | $59 / month | Up to 400 | Everything in Starter, plus one extra channel (Slack, Teams, Azure DevOps or webhook), CSV export and priority support |
Prices are in US dollars. The limits count the app registrations found in the tenant and are not hard cut-offs: a customer above a limit is asked to move to the plan that fits, and their access is not blocked.
As a CSP partner you set the price you charge your customer. The plans and prices available to resell in your market are on the Marketplace listing. To discuss partner margin through an ISV-to-CSP private offer, email us.
Logos and screenshots
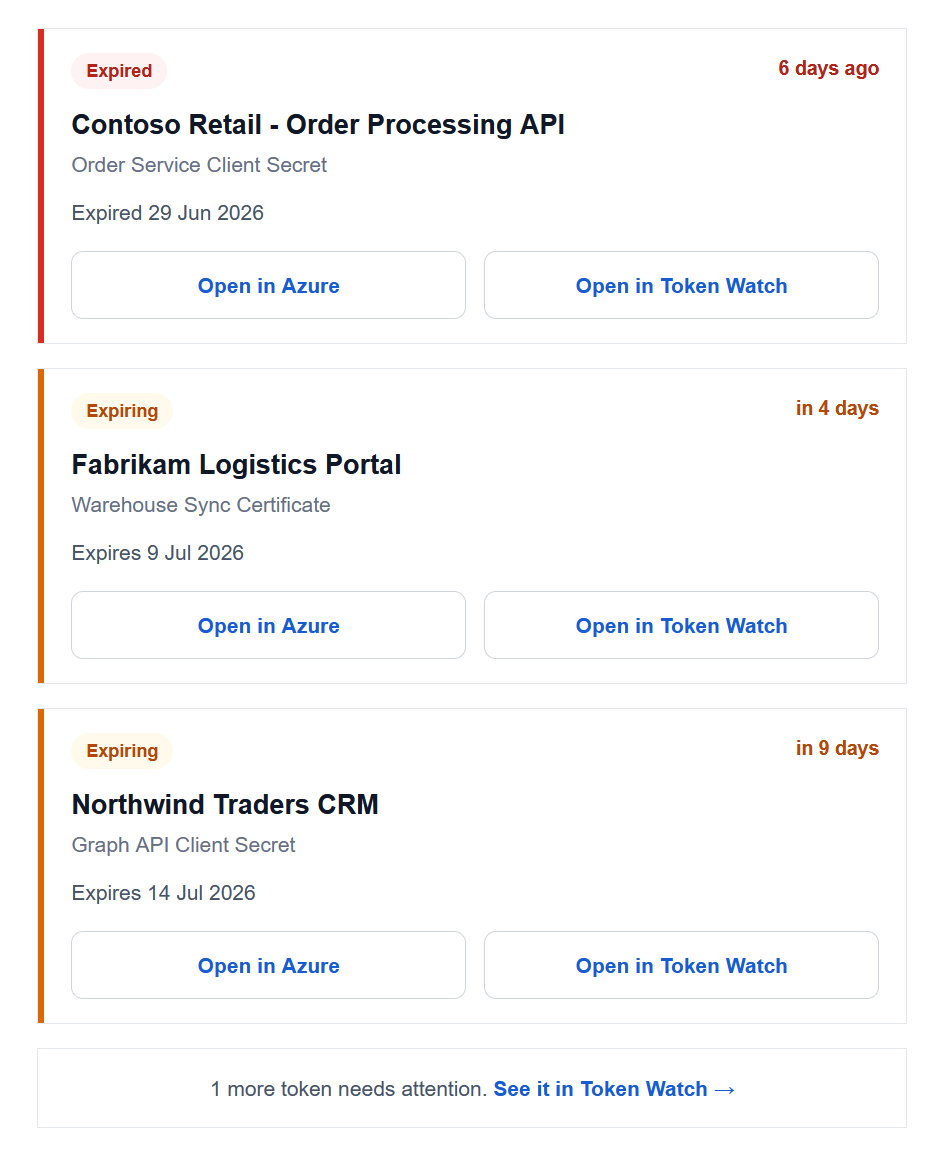
Right-click an image and save it, or open it in full size from the link underneath. Write the product name as Token Watch, two words. Please don't recolor, stretch or crop the logo, and don't suggest that Microsoft makes Token Watch: it is an independent product sold through Microsoft Marketplace.

Pages to send customers
- Product overview and pricing
- Documentation, starting with connecting a tenant
- Security review pack for the customer's security team
- How to get notified before an Entra app registration secret expires, which compares scripts, Entra's own emails and Token Watch
- Fix AADSTS7000222, for customers already dealing with an outage
Partner contact
Email contact@aztokenwatch.com with "CSP" in the subject line. We can help with private offers, a walkthrough for your sales team, or a security questionnaire for one of your customers. You'll hear back within 48 hours.